A ransomware Trojan that gets installed on a computer as a module of Trojan.Gapz.1. The Trojan can capture an image from a web camera connected to a computer and display it on the ransomware screen once access to Windows is blocked.
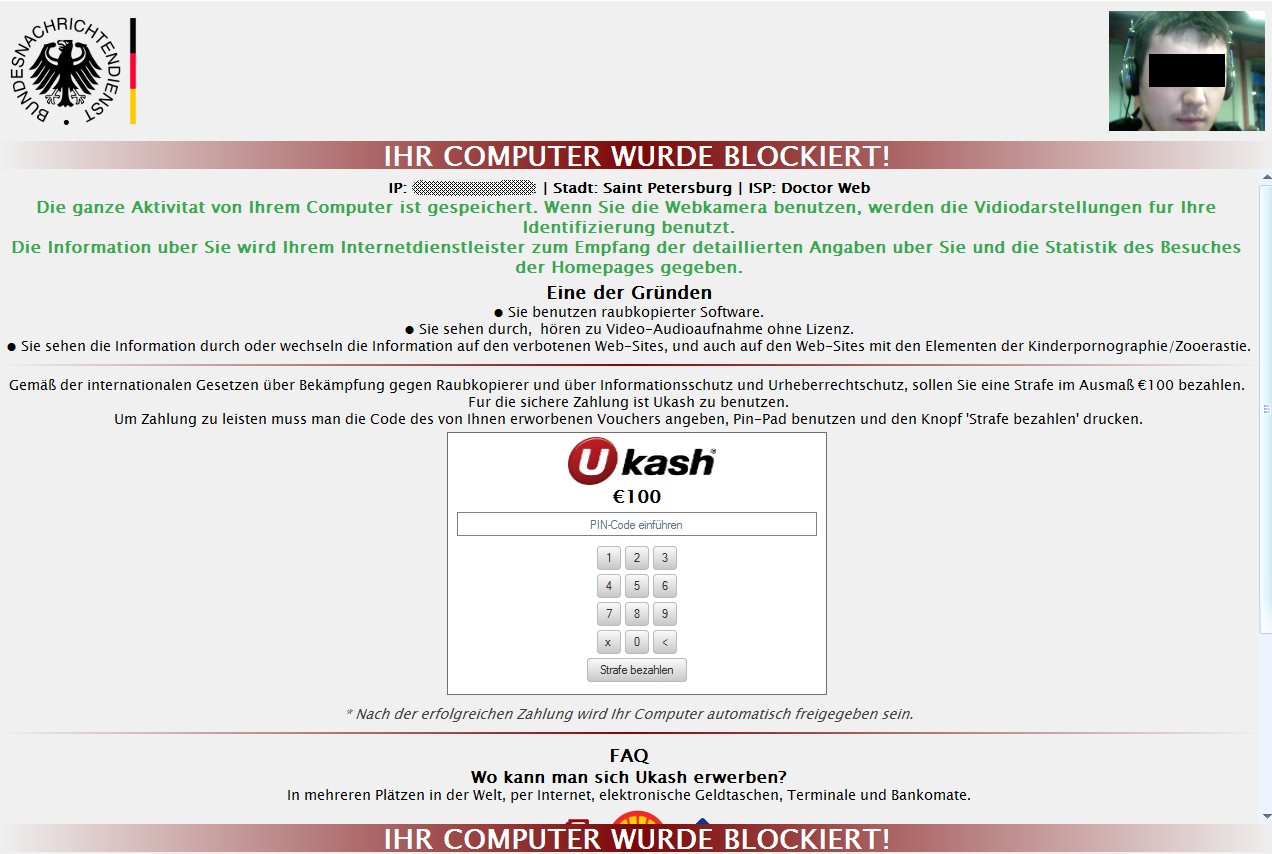
During installation, the Trojan performs the following actions:
- Decrypts the configuration file containing information on countries where the malware can operate and payment systems that the Trojan can target.
- Generates a unique ID and sends it together with computer-related information to the remote command and control server.
- Receives WHIOS information on the infected computer ID.
- Compares this data with the country list from the configuration file and locks the computer only if it is located in Canada, Spain, Germany, France, Italy, Portugal, Austria, Switzerland, Great Britain, Australia or the USA.
- Sends the command and control server a new request and gets the bot ID as a reply.
- Sends another request and downloads from the server several XML files based on which it generates an image and text for the ransomware message.
The malware can target the following payment systems:
- Ukash
- Moneypack
- Paysafecard
To unlock the computer, the Trojan demands that the victim enter a ransom payment transaction code. The entered code is transmitted to the command and control server to be validated.